RiverSweeps.cloud Privacy Policy: scope, evidence and the right next step
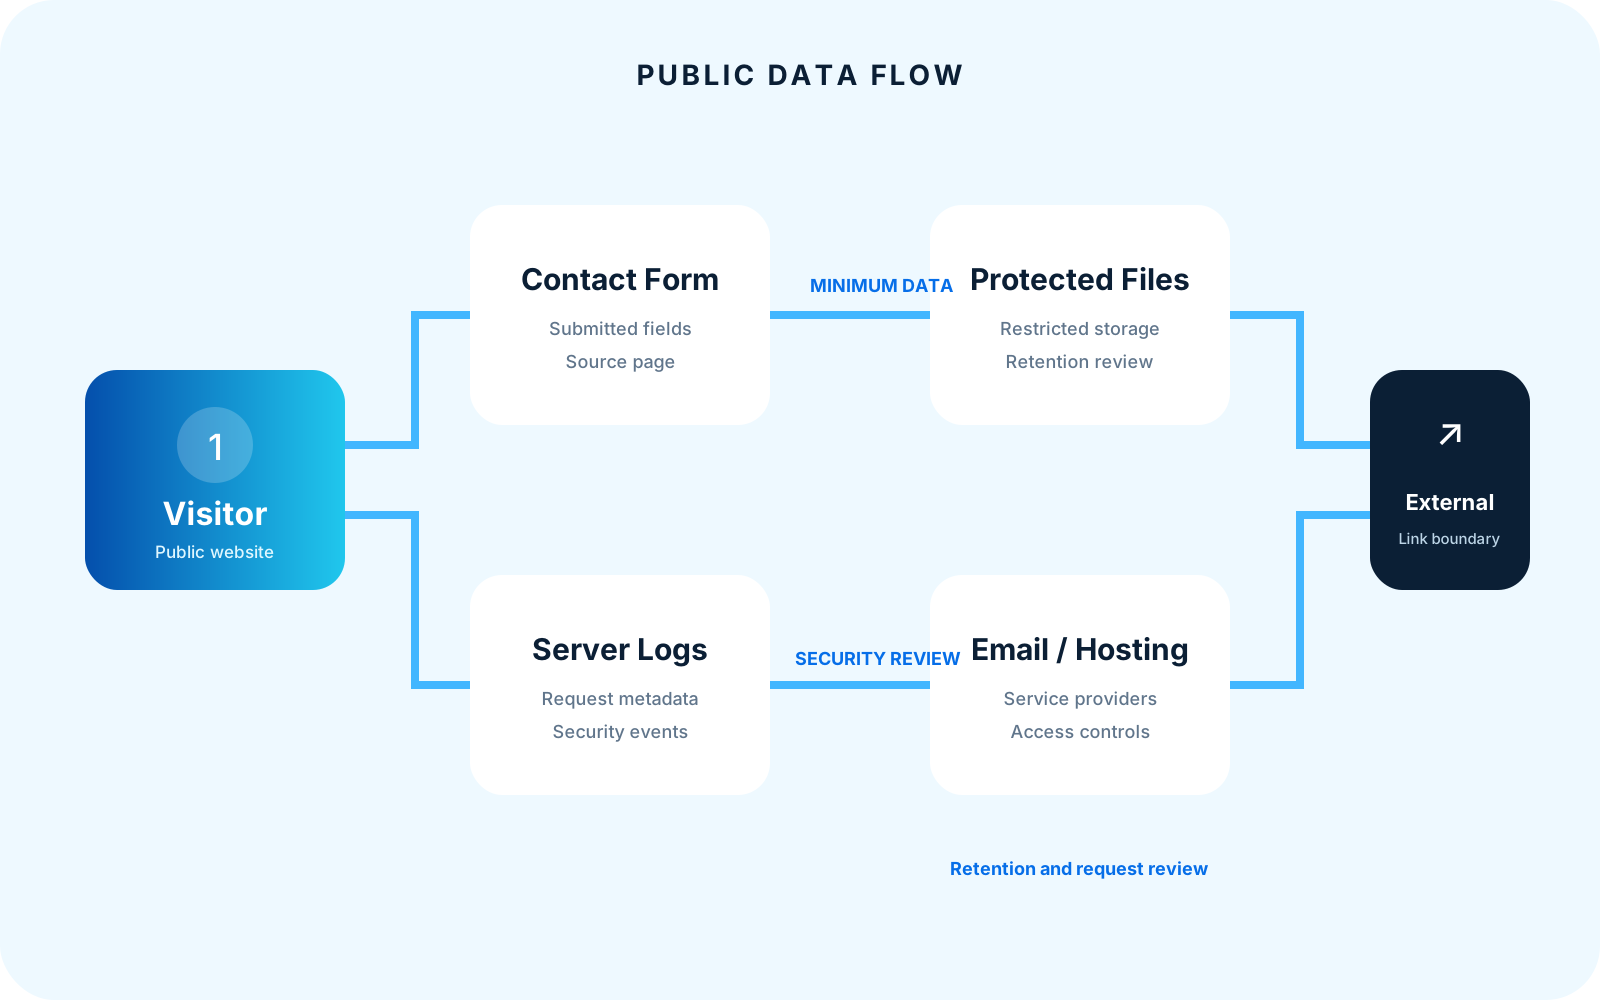
A privacy policy should describe what the website actually does, not what a generic template assumes. RiverSweeps.cloud currently presents public content, can store contact requests in protected flat files, may email a copy when configured and can link or embed third-party ecosystem destinations. Each function creates a different data path that must be inventoried and verified.
This editorial draft maps public form submissions, server logs, security processing, communications, service providers, retention and privacy requests. It must be reconciled with the actual hosting, analytics, email, embeds, cookies, lead handling, applicable laws and legal entity before publication as a final policy.
Understand this data flow alongside RiverSweeps.cloud Terms of Use, RiverSweeps accessibility and RiverSweeps compliance information.
This material is an editorial framework for counsel and site owners. It explains the real website or deployment context in plain language, but the final legal effect depends on the correct entity, jurisdiction, facts and qualified review.
Who this guide is for
The same RiverSweeps page can be discovered by people with very different responsibilities. The table below identifies the intended readers and the decision each one should be able to make after reading.
| Reader | What this page should help them determine |
|---|
| Visitors | Need to know which information is processed when they browse or submit a form. |
|---|
| Prospects and reporters | Need safe submission guidance and a route for applicable privacy requests. |
|---|
| Site administrators | Need retention, access, backup, email and incident responsibilities. |
|---|
| Counsel and vendors | Need an accurate data map, legal basis, contracts and jurisdiction analysis. |
|---|
When a question moves beyond privacy practices for the public RiverSweeps.cloud website, follow the contextual links near the end of this guide. That separation is intentional: a player route, a device installer, a protected dashboard and a commercial consultation should never be presented as if they were the same task.
What to evaluate in practice
Use the following points as a working agenda. They are written to expose handoffs, assumptions and evidence that a short feature list usually misses.
Inventory collection by source
Separate data typed into forms from ordinary server logs, security records, analytics, cookies, embedded content and messages handled by email or other channels.
During a demonstration, ask the presenter to show this point in context and explain who owns the decision after launch. For RiverSweeps.cloud Privacy Policy, the answer should remain consistent with the page's stated scope and should not become a promise about unrelated accounts, locations or product versions.
For specific requests and official destinations, use official RiverSweeps websites, RiverSweeps product facts and RiverSweeps privacy contact.
Describe purposes specifically
Contact data may be used to route a request, respond, maintain business records and protect the site. Do not claim uses the organization has not implemented or omit marketing if it actually occurs.
Record the answer with the configuration, device or page version so it can be checked when the environment changes. For RiverSweeps.cloud Privacy Policy, the answer should remain consistent with the page's stated scope and should not become a promise about unrelated accounts, locations or product versions.
Map every recipient
Hosting, email, security, analytics and ecosystem teams may process data. Identify service-provider roles and avoid saying ‘never shared’ when routing a request necessarily involves another responsible team.
The useful evidence is a current screen, defined report, measured location, written process or responsible first-party owner—not an adjective. For RiverSweeps.cloud Privacy Policy, the answer should remain consistent with the page's stated scope and should not become a promise about unrelated accounts, locations or product versions.
Set retention from need
Flat-file leads, mailboxes, backups and logs can have different periods. Define owners and deletion paths instead of promising immediate deletion that backups cannot support.
If the answer varies by operator or jurisdiction, publish that limitation beside the claim instead of hiding it in a generic footer. For RiverSweeps.cloud Privacy Policy, the answer should remain consistent with the page's stated scope and should not become a promise about unrelated accounts, locations or product versions.
Respect sensitive-data limits
The public form should tell users not to submit passwords, codes, payment details, identity documents or unnecessary player information. Administrative access and backups must reinforce that boundary.
A buyer should be able to repeat the workflow with a representative role and understand the expected result without privileged improvisation. For RiverSweeps.cloud Privacy Policy, the answer should remain consistent with the page's stated scope and should not become a promise about unrelated accounts, locations or product versions.
Address third-party destinations
When a visitor loads an embed or follows a River777, Bet777, RiverSlot or other link, another service may process information under its own policy. Use deliberate loading and clear links where practical.
This distinction also keeps neighboring RiverSweeps pages focused and reduces the chance that several URLs answer the same search question with nearly identical copy. For RiverSweeps.cloud Privacy Policy, the answer should remain consistent with the page's stated scope and should not become a promise about unrelated accounts, locations or product versions.
A practical evaluation workflow
A structured review prevents an attractive screenshot or isolated feature from becoming the entire buying decision. Keep the notes, sample roles and dates together so the decision can be revisited.
- Step 1. Create a current data-flow inventory for forms, logs, email, analytics, embeds, backups and vendors. Document the person responsible, the evidence collected and any assumption that still needs product, operational or legal confirmation.
- Step 2. Confirm the legal entity, contact, purposes, legal bases and categories of recipients with counsel. Document the person responsible, the evidence collected and any assumption that still needs product, operational or legal confirmation.
- Step 3. Set retention and deletion procedures for every storage location, including backups and mailboxes. Document the person responsible, the evidence collected and any assumption that still needs product, operational or legal confirmation.
- Step 4. Test privacy-request identity verification and avoid disclosing data to an unverified requester. Document the person responsible, the evidence collected and any assumption that still needs product, operational or legal confirmation.
- Step 5. Review the policy after adding a tool, changing providers, enabling marketing or altering a player embed. Document the person responsible, the evidence collected and any assumption that still needs product, operational or legal confirmation.
Do not skip the exception path. A normal demonstration proves that the designed route can work; an exception demonstrates whether staff can pause safely, preserve context, obtain approval and continue without exposing credentials or private records.
Evidence to request and retain
The appropriate record depends on the page, but every material claim should be connected to something current and reviewable. Replace sample or conceptual media with authentic, anonymized RiverSweeps material before using it as product proof.
| Evidence | What a useful record contains | Why it matters |
|---|
| Data map | Collection source, fields, purpose, storage, recipients, retention and security owner. | It turns a general claim into something another reviewer can verify. |
|---|
| Vendor record | Service, role, contract, location and deletion or export capability. | It makes changes in scope, version or responsibility visible. |
|---|
| Form minimization | Only fields needed to route and answer the request. | It reduces disagreement when a workflow or page is reviewed later. |
|---|
| Retention schedule | Separate periods for leads, email, security logs and backups. | It gives support enough context without requiring protected information. |
|---|
| Request process | Access, correction, deletion or other applicable rights with proportionate verification. | It distinguishes current first-party evidence from a copied market claim. |
|---|
| Change trigger | A documented review when tools, embeds, marketing or legal requirements change. | It creates a clear trigger for maintenance, correction or re-approval. |
|---|
Questions for a RiverSweeps demonstration or review
Ask these questions against a representative configuration. A credible answer can state that a detail is unknown or variable, provided the owner and verification path are clear.
- What data does the live site collect today, including logs and third-party tools? Ask to see the answer, not only hear a description.
- Where does each field go after the user presses Submit? Record the scope and date attached to the response.
- Which team or provider receives the data and for what purpose? Identify which role owns the decision after deployment.
- How long does it remain in live storage, email and backups? Confirm whether the answer changes by device, operator or market.
- How is a privacy requester verified without collecting excessive new data? Request a redacted example or primary source where appropriate.
- Which feature change would make the current policy inaccurate? Note the event that would require the answer to be reviewed again.
Common mistakes and how to avoid them
The following risks are not reasons to abandon a useful product or page. They are reasons to make the decision with better boundaries and evidence.
A promise that data is not shared may be false if email, hosting or another ecosystem team processes it.
Avoid it by assigning an owner and checking the real environment before publication or purchase. The correction should be visible in the workflow, content or approval record rather than left as an informal assumption.
A policy cannot compensate for a form that requests unnecessary sensitive information.
Reduce the risk with a representative pilot, documented scope and a clear escalation path. The correction should be visible in the workflow, content or approval record rather than left as an informal assumption.
Deleting one flat file may not remove a mailbox or backup copy.
Keep the statement conditional until current first-party evidence supports it. The correction should be visible in the workflow, content or approval record rather than left as an informal assumption.
Loading a third-party player frame can create a separate data relationship.
Separate the responsible page or role instead of forcing one answer to cover every audience. The correction should be visible in the workflow, content or approval record rather than left as an informal assumption.
Security details should be meaningful without exposing defenses.
Use the minimum information and access needed for the task, then review the record. The correction should be visible in the workflow, content or approval record rather than left as an informal assumption.
This editorial draft requires legal and operational validation before final publication.
Pause expansion when the facts, permission or support owner are not yet clear. The correction should be visible in the workflow, content or approval record rather than left as an informal assumption.
Build a decision record
For RiverSweeps.cloud Privacy Policy, a decision record should name the intended audience, the problem being solved, the chosen configuration or content scope, the rejected alternatives and the evidence used. It should also list unresolved questions and the date on which the decision must be reviewed.
Separate observation from prediction. A current interface, measured floor, completed test or defined report is an observation. Expected adoption, savings, retention, revenue or legal treatment is a prediction and needs its own support. This distinction keeps marketing persuasive without turning it into an unsupported guarantee.
Use representative conditions. A perfect network, unrestricted demonstration account, empty store or desktop-only preview can hide the work that appears during an ordinary shift. Include at least one realistic constraint and one recoverable exception.
Finally, identify the change triggers: a new market, new device class, new game mode, new account hierarchy, new data recipient, material interface change or revised promotion. A previous approval should not silently cover facts it never reviewed.
Related RiverSweeps resources
These links are descriptive by design. They let readers and search systems understand the destination before following it, while keeping this page focused on its own question.
Bottom line
Publish the privacy policy only after the data map matches the live system. Clear collection, purpose, recipients, retention and request handling are more trustworthy than broad assurances a technical owner cannot verify.
Confirm variable product details in a current RiverSweeps demonstration and obtain qualified advice for the complete promotion and jurisdiction. Public information should help the next decision; it should never disguise an unresolved one.
First-party audience measurement and traffic security
RiverSweeps.cloud uses a self-hosted analytics system to understand page visits, browser sessions, referrers, approximate country signals resolved locally with a MaxMind GeoLite2 Country database, and automated traffic. It does not use an advertising analytics platform, cross-site advertising identifiers, canvas fingerprinting, or sell analytics data.
Client IP addresses are transformed into keyed one-way identifiers before analytics data is stored. A short-lived first-party session cookie helps distinguish a browser session from individual page requests. Browser engagement is confirmed after the page remains active for several seconds. Do Not Track and Global Privacy Control signals are respected for browser visitors.
When software claims to be a supported search crawler, the site may perform reverse DNS and a matching forward DNS lookup to confirm the crawler identity. The operator may block abusive traffic by protected visitor identifier, country, bot family, or user-agent rule. Analytics event files are stored locally and removed according to the retention setting shown in the protected administration area.